

Cyber Insurance
Cyber Insurance Isn't Enough: What Insurers Won't Tell You About Coverage Gaps
A cyber policy pays on what you declared, not on what you think you bought. What it pays, what it never will, France's 72-hour rule and a 30-minute check.
In May 2022, International Control Services, a company in Illinois, was hit by ransomware. Its cyber insurer, Travelers, did not argue about the attack. It went to court over the application form. ICS had stated that it required multi-factor authentication to access email, and, according to Travelers, across its other systems too. Travelers alleged that MFA in fact protected only the firewall. Seven weeks after the suit was filed, both sides asked the court to treat the $1 million policy as null and void from its inception.
That case is the coverage gap the usual warnings miss. Insurers do tell you what they won’t cover. They write it down — in the exclusions, the sublimits, and above all in the security questions they asked before quoting. A cyber policy pays on what you declared, not on what you think you bought. The claim that fails on a declaration is the one nobody sees coming, because the company wrote the gap itself.
The proposal form is part of the policy
Before quoting, an insurer asks a list of security questions. Is MFA enforced on remote access and administrator accounts? Are backups kept offline or immutable? Is endpoint detection deployed and monitored? How fast are critical patches applied? Your answers set the price and the decision to insure. After an incident, they become the yardstick for the claim.
French insurance law spells out what follows. Article L113-2 of the Code des assurances obliges the insured to answer the insurer’s questions accurately. If a false answer was intentional and changed the insurer’s view of the risk, Article L113-8 makes the contract void and lets the insurer keep the premiums, even if the misstatement played no part in the loss. If the answer was wrong in good faith and the error only surfaces after a claim, Article L113-9 cuts the payout in proportion to the premium that should have been charged.
The good-faith case is the common one. Nobody lied. MFA was switched on for email when the form was signed, and the VPN was left for later. The backup marked “offline” is a storage box joined to the same domain as everything else. The endpoint detection is deployed, and its alerts land in an inbox nobody reads. The patching deadline on the form is the one in the policy document, never measured. Each answer was roughly true on the day someone ticked it. After an incident, a forensic team checks whether it was true on the day of the attack.
What a cyber policy actually pays for
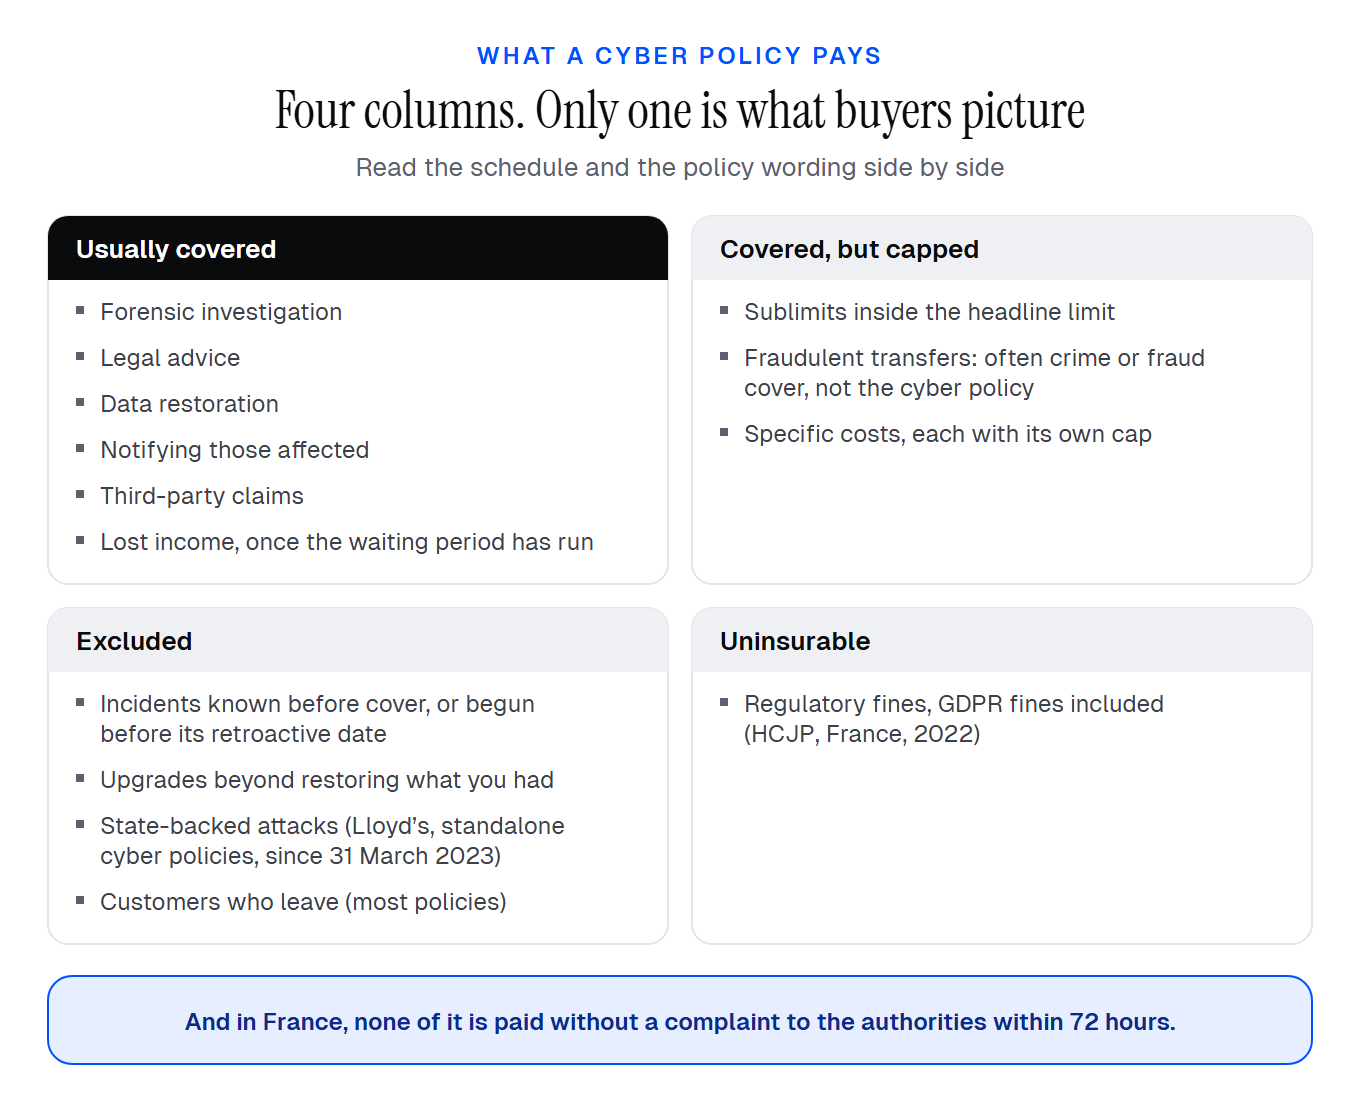 Read the schedule and the wording side by side and the cover sorts into four columns. Only the first is what most buyers picture.
Usually covered. The cost of responding: forensic investigation, legal advice, data restoration, notifying the people affected, and claims from third parties. Lost income while systems are down is usually covered too, but only once a waiting period, set in hours in your schedule, has run.
Covered, but capped. Sublimits sit inside the headline limit. The one that surprises finance teams most is fraud. A transfer to a criminal’s account after a fake supplier email usually falls under crime or fraud cover rather than the cyber policy, if it is insured at all. We set out who pays in each case in our article on business email compromise.
Excluded. Incidents you knew about before the policy started, or that began before its retroactive date. Upgrades beyond restoring what you had. And attacks attributed to a state. War exclusions written for armies did not fit malware well, and Merck won its NotPetya case on that point before a New Jersey appeals court in May 2023. The market had already moved: since 31 March 2023, Lloyd’s has required its syndicates to include a state-backed cyber-attack exclusion in standalone cyber policies, with an agreed basis for attributing the attack.
Uninsurable. Regulatory fines. In France, the Haut Comité Juridique de la Place financière de Paris concluded in 2022 that administrative fines and pecuniary sanctions, GDPR fines included, cannot be insured under current law. Its reasoning covers administrative fines generally, so we would not expect a French policy to pay a NIS2 fine either once the law is in force. And most policies pay nothing for the customers who leave.
France adds a 72-hour condition
Since 24 April 2023, Article L12-10-1 of the Code des assurances has made any payment under a cyber clause conditional on one step: the victim must file a complaint with the authorities no later than 72 hours after becoming aware of the attack. It applies to companies, and to individuals acting in a professional capacity, for losses caused by the intrusions, sabotage and data tampering defined in Articles 323-1 to 323-3-1 of the Penal Code.
Seventy-two hours is also the GDPR’s window for notifying the CNIL of a personal data breach. In the worst weekend of the year, two clocks start at once, and the complaint is the step an incident plan most easily leaves out. Put it in yours: who files it, where, and with which facts ready. We map how the regulatory clocks run together in One incident, three regulators.
Outside France the specific rule differs, but every policy carries notice conditions: how quickly you must tell the insurer, which number you call, and which providers you may engage before approval. Read them before the incident, not during it.
What the board still owns
Insurance moves part of the cost of an incident. It does not move the decisions behind it. Where NIS2 is in force — Belgium, Germany and Luxembourg among others — Article 20 adds two separate duties: the management body must approve the cybersecurity risk-management measures and oversee their implementation, and it can be held liable for the entity’s infringements of Article 21. Insurance does not carry the oversight, and in France it cannot carry an administrative fine either. As of late October 2026, France has not transposed NIS2: the bill was withdrawn from the National Assembly’s agenda on 6 October with no new date set.
The size of the cover is a board decision too. AMRAE’s LUCY 2026 study puts the average limit for a French company with €10–50 million of turnover at €1.4 million in 2025, with an average deductible of about €11,000, and that average limit fell by a fifth during the year. Claims are real: insurers in the study paid €83.2 million on 1,251 claims in 2025, 53% more than in 2024. Set €1.4 million against your own estimate of two weeks offline, a forensic team and a rebuild, and decide deliberately what you carry yourself.
A 30-minute declaration check
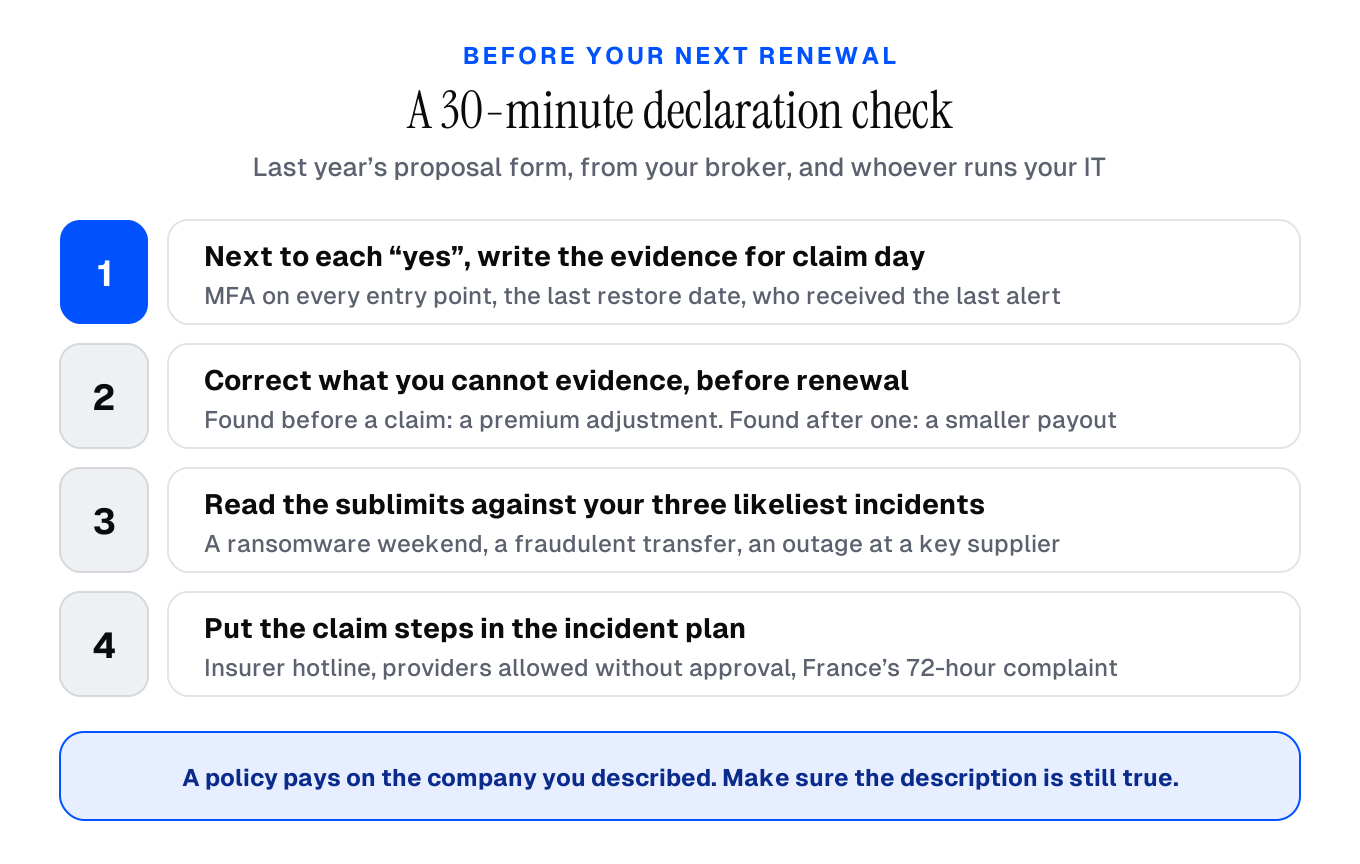 A 30-minute declaration check: every “yes” on the proposal form, next to the evidence you would show on claim day.
Ask your broker for last year’s proposal form and go through it with whoever runs your IT.
- Next to each “yes”, write the evidence you would show on claim day. MFA: the list of every remote entry point and administrator account, with MFA enforced on each. Backups: the date of the last restore from the offline copy. Endpoint detection: who received the last alert, and when.
- Correct any answer you cannot evidence, before renewal. Under Article L113-9, an inaccuracy found before a claim leads to a premium adjustment or, at worst, the end of the contract. Found after a claim, it cuts the payout.
- Read the sublimits against your three likeliest incidents: a ransomware weekend, a fraudulent transfer, an outage at a key supplier. Write down what each would pay and what you would carry.
- Put the claim steps in the incident plan: the insurer’s hotline, the providers you may engage without approval, and, in France, the 72-hour complaint.
None of this needs a purchase. It needs someone who did not fill in the form to check it. That independence is what our internal audit services are built around, and owning the answers at each renewal is part of what our Virtual CISO service does.
Take the next step
Talk to a security practitioner, not a salesperson.
Twenty-five minutes, no slide deck, no follow-up sequence. We'll talk through where you are, what's coming up next on your regulatory horizon, and whether we can help.