GDPR
Paper compliance is not security. It isn't compliance either.
GDPR, NIS2, PCI DSS and ISO 27001 now ask whether your controls work. After a breach, a control that exists only on paper fails both tests.
In January 2026 the French data protection authority, the CNIL, fined France Travail €5 million after a breach. The finding that should worry every board is not the size of the fine. It is this: France Travail’s own impact assessments had identified most of the right security measures. They had not been implemented.
That is the case the old line, compliance is not security, is meant to explain. The line is half right. Where it goes wrong is the conclusion people draw from it: that the gap belongs to the frameworks, which ask for paperwork while attackers exploit reality. That is no longer a fair reading of the texts. The major frameworks now ask whether your controls work, and after a breach the regulator reads them exactly that way. A control that exists only on paper fails the attacker and the regulator at once.
The excuse the title gives you
Nobody serious disputes that compliance is a floor. The trouble with the sentence is what it lets a management team conclude after an incident: we did what the rules asked, and the rules were not enough.
That conclusion assumes the rules only ever asked for documents. Read GDPR, NIS2, PCI DSS and ISO 27001 as they stand today and each one asks a second question. Not do you have it, but does it work, and how do you know. A programme that can answer only the first question is not secure. Under most of these texts, it is not compliant either.
Four texts, one question: does it work
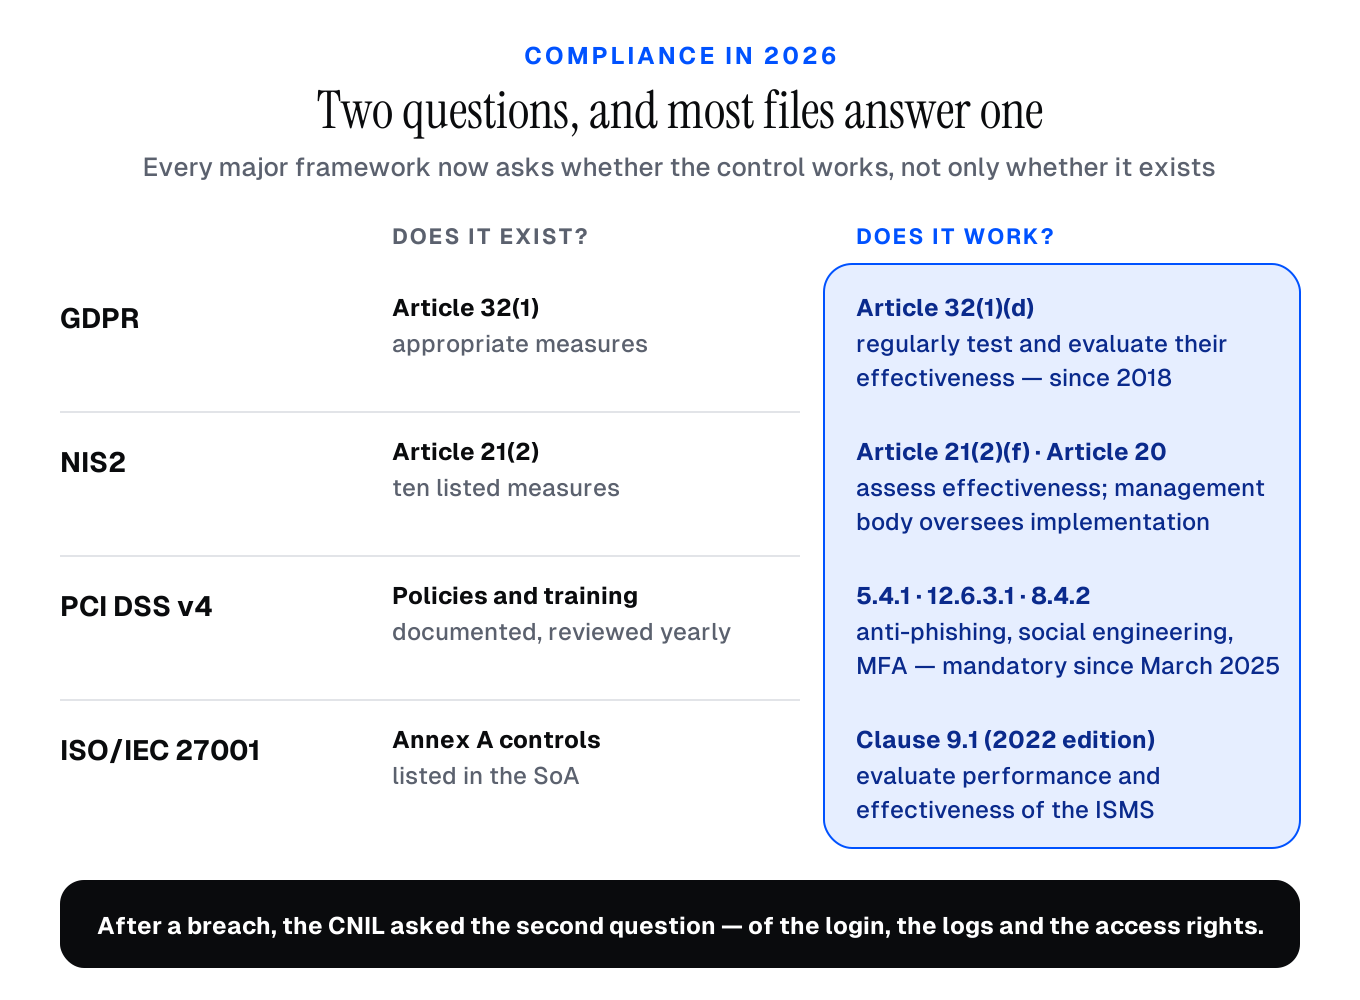 Every major framework now asks two questions. Most compliance programmes only answer the first.
GDPR. Article 32 is usually summarised as “appropriate technical and organisational measures”, and left there. Article 32(1)(d) goes further: among the measures to implement as appropriate, it names “a process for regularly testing, assessing and evaluating the effectiveness” of those measures. It has applied since 2018. A GDPR programme with policies and no test evidence is not a security gap sitting beside a compliant file. The file is incomplete.
NIS2. Article 21(2) lists ten measures. Among them, (f) requires policies and procedures to assess the effectiveness of the cybersecurity risk-management measures, and (j) requires multi-factor authentication or continuous authentication where appropriate. Article 20 then adds two separate duties: the management body must approve the measures and oversee their implementation, and it can be held liable for the entity’s infringements of Article 21. Where NIS2 is in force, “we had a policy” does not answer “did you oversee it working”. It is in force in Belgium, Germany and Luxembourg, among others. As of late October 2026 France has still not transposed it: the bill was withdrawn from the National Assembly’s agenda on 6 October with no new date set.
PCI DSS. The older complaint about PCI DSS was that it ignored social engineering. That stopped being true on 31 March 2025, when the future-dated requirements of version 4 became mandatory. Requirement 5.4.1 now demands processes and automated mechanisms to detect and protect personnel against phishing. Requirement 12.6.3.1 requires awareness training on phishing and social engineering. Requirement 8.4.2 requires multi-factor authentication for all non-console access into the cardholder data environment. If your PCI DSS assessment still predates those requirements, so does your picture of what it covers.
ISO/IEC 27001. The 2022 edition’s clause 9.1 requires the organisation to evaluate the information security performance and the effectiveness of its management system. A certificate is not a statement that controls exist. It is a statement that a management system measures whether they work.
What the regulator checked after the breach
The clearest evidence of how these texts are read comes from enforcement, and in 2026 the most detailed enforcement record is still the GDPR’s.
The CNIL fined Free Mobile and Free €42 million in total (€27 million and €15 million) over an October 2024 breach that reached 24 million subscriber contracts. Under Article 32 it found that the authentication procedure for the companies’ VPN was not robust enough, that the measures for detecting abnormal behaviour were ineffective, and that certain elementary security measures were missing.
The France Travail decision followed the same month. In the first quarter of 2024, attackers used social engineering to take over accounts belonging to CAP EMPLOI advisers. The CNIL found that their authentication was not robust enough, that logging could not adequately detect abnormal behaviour, and that access rights had been defined too broadly. It then made the finding quoted at the top of this article: most of the measures had been identified, and had not been implemented. The fine came with an order to justify corrective measures on a fixed timetable, under a penalty of €5,000 for each day of delay. The CNIL closed that order on 23 September 2026, without collecting the penalty, once the corrections had been justified.
Read side by side, the two decisions turn on three things: how people log in remotely and whether the logs can detect an intruder, in both cases, and whether access rights match what each person needs, at France Travail. None of the three is exotic. In each case the authority’s question was whether the control had worked on the day.
Where the frameworks genuinely stop
The frameworks do have real limits, and it is worth being exact about them rather than general.
You draw the scope. PCI DSS covers the cardholder data environment, and an ISO 27001 certificate covers the scope you chose to certify. An attack can land on a system outside both.
The audit samples. A certification auditor sees a sample of evidence over a few days. An attacker needs one account the sample never touched.
No framework names your adversary. They are written to be threat-neutral. Deciding who would come for you, and how, is the job of your risk assessment, which is precisely the step most often done superficially.
These are reasons to read the frameworks properly, not to dismiss them. The work that serves one regulator usually serves the others: we set out how the same evidence answers ISO 27001, NIS2 and DORA in One ISMS, three regulators: the same nine documents.
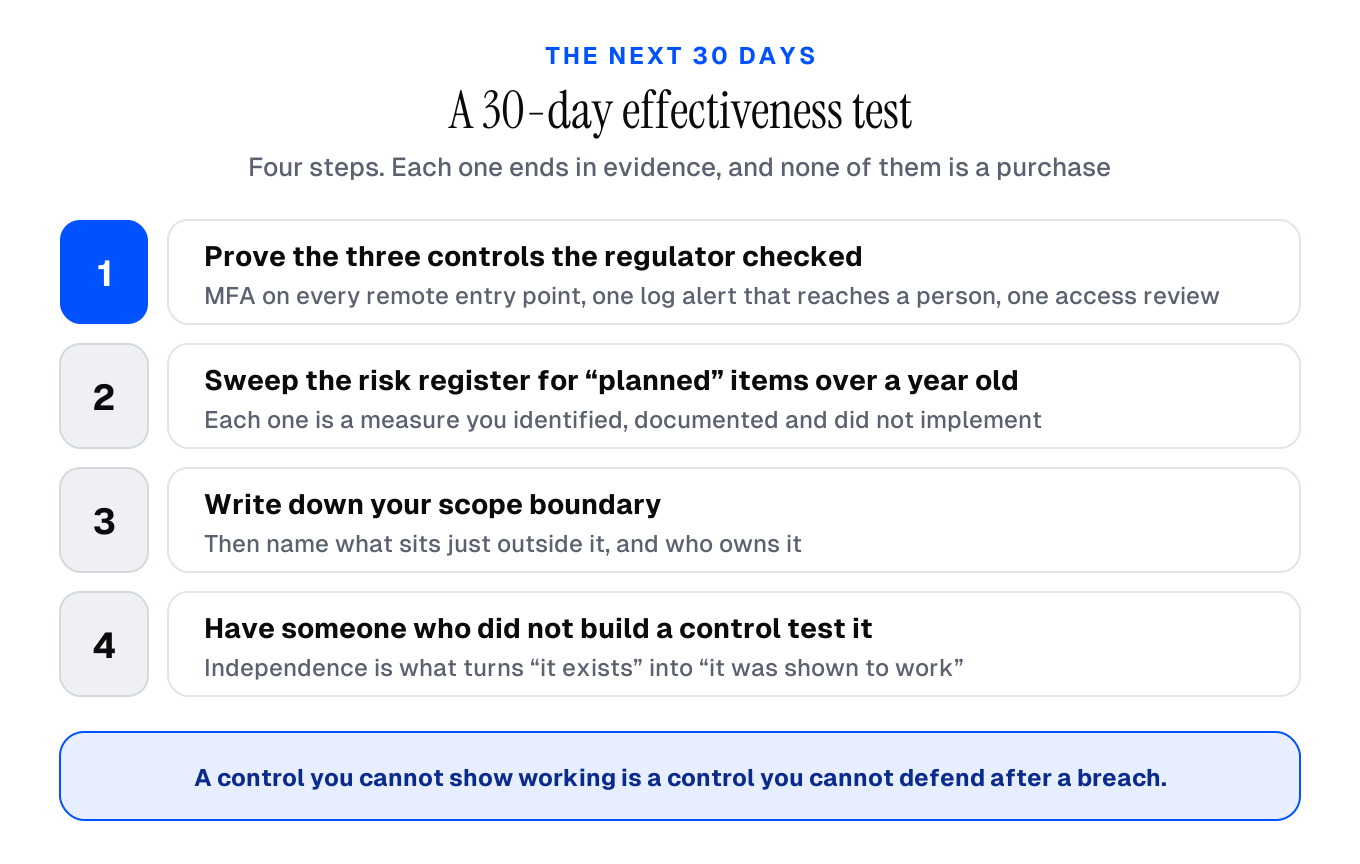 A 30-day effectiveness test. It needs evidence, not new tools.
- Prove the three controls the regulator checked. List every remote entry point and show multi-factor authentication on each. Trigger one test event and confirm a log alert reaches a person. Review access rights on one sensitive system against what each user actually needs.
- Sweep the risk register for anything marked “planned” for more than a year. Each one is a measure you have identified, documented and not implemented. That is the France Travail finding, written in your own hand.
- Write down your scope boundary. Then name what sits just outside it and who owns it.
- Have someone who did not build a control test it. Independence is what turns a control that exists into one shown to work. That is what our NIS2 readiness work and internal audits are built around.
None of these steps involves a purchase. Each produces evidence you can put in front of a board, an auditor or a regulator.
Take the next step
Talk to a security practitioner, not a salesperson.
Twenty-five minutes, no slide deck, no follow-up sequence. We'll talk through where you are, what's coming up next on your regulatory horizon, and whether we can help.